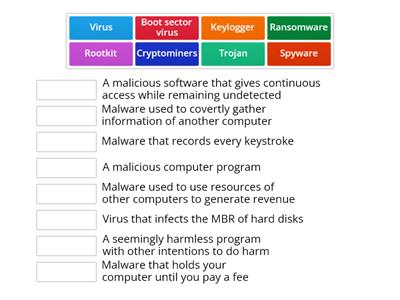
Virus, Self-replicating program that attaches to legitimate files., Worm, Standalone malware that spreads through networks automatically., Trojan, Malware disguised as a legitimate program to trick users into running it., RAT, Remote Access Trojan allowing full control over an infected system, Backdoor, Unauthorized access method to a system, bypassing security mechanisms, Botnet, A network of infected devices controlled remotely., Logic Bomb, A hidden malicious code that triggers under specific conditions., Rootkit, Stealthy malware that hides its presence and allows continued access., Zero-Day, A previously unknown software vulnerability exploited by attackers., Advanced Persistent Threat, Long-term cyber espionage targeting organizations or governments., Ransomware, Encrypts files and demands payment for decryption., Spyware, Secretly gathers user information and sends it to an attacker., Adware, Displays unwanted advertisements, often in a deceptive manner., SPAM, Unsolicited bulk email, often containing phishing or malware links., Adware Example, Fireball - Hijacked web browsers to generate ad revenue and install additional malware., Ransomware Example, CryptoLocker - Encrypted user files and demanded Bitcoin payments for decryption keys., Backdoor Example, Back Orifice - Provided remote administrative control over Windows machines., Virus Example, Mydoom - Spread through email attachments, performing mass email spamming and launching DDoS attacks., Worm Example, WannaCry - Exploited a Windows vulnerability to spread ransomware, encrypting user files and demanding payment., SPAM Example, Love Bug (ILOVEYOU) - Spread through email with an infected attachment, overwriting files and sending itself to contacts., Spyware Example, Pegasus - Highly sophisticated spyware used for the surveillance of journalists and activists., Advanced Persistent Threat Example, APT28 (Fancy Bear) - Russian state-sponsored hacking group targeting political organizations., Zero-Day Example, Aurora Exploit - Used to attack Google and other tech firms by exploiting an Internet Explorer vulnerability., Rootkit Example, Stuxnet - Targeted Iranian nuclear facilities by manipulating industrial control systems., Logic Bomb Example, CIH (Chernobyl) - Activated on specific dates, overwriting hard drives and BIOS firmware., Botnet Example, Mirai Botnet - Infected IoT devices to launch massive DDoS attacks., RAT Example, DarkComet - Allowed attackers to spy on victims, log keystrokes, and control webcams remotely., Trojan Example, Zeus Trojan - Stole banking credentials by logging keystrokes and intercepting online transactions.
0%
Malware & Examples
Condividi
Condividi
di
Jscurtis
High
CS
Modifica contenuto
Salva
Mi piace
Stampa
Incorpora
Altro
Compiti
Classifica
Mostra di più
Mostra meno
Questa classifica è privata. Fai clic su
Condividi
per renderla pubblica.
Questa classifica è stata disattivata dal proprietario della risorsa.
Questa classifica è disattivata perché le impostazioni sono diverse da quelle del proprietario della risorsa.
Ripristina le opzioni
Abbinamenti
è un modello a risposta aperta. Non genera punteggi validi per una classifica.
Login necessario
Stile di visualizzazione
Tipi di caratteri
Abbonamento richiesto
Opzioni
Più così
Comptia A+ Core 2 - 7 steps of Malware Removal Process
di
Margaritastudying
Abbinamenti
56
Security+: Malware Types
di
Terry22
Abbinamenti
23
Malware
di
Benzi
Abbinamenti
5
Network Attacks 11.6 Vocab
di
Benzi
Organizza per gruppo
3
DayDayUp IT Course - Lesson 27 - Malware vocabulary
di
Schooldaydayup
Flash card
3
Malware - Comptia A+ 1102
di
Jesus38383
Abbinamenti
85
malware
di
23tomla12
Abbinamenti
5
Computer Security Words
di
Educoot
Quiz
3
Cambia modello
Mostra tutto
Apri risultati
Copia link
Codice QR
Elimina
Ripristinare il titolo salvato automaticamente:
?